
Why it's built this way
Headline
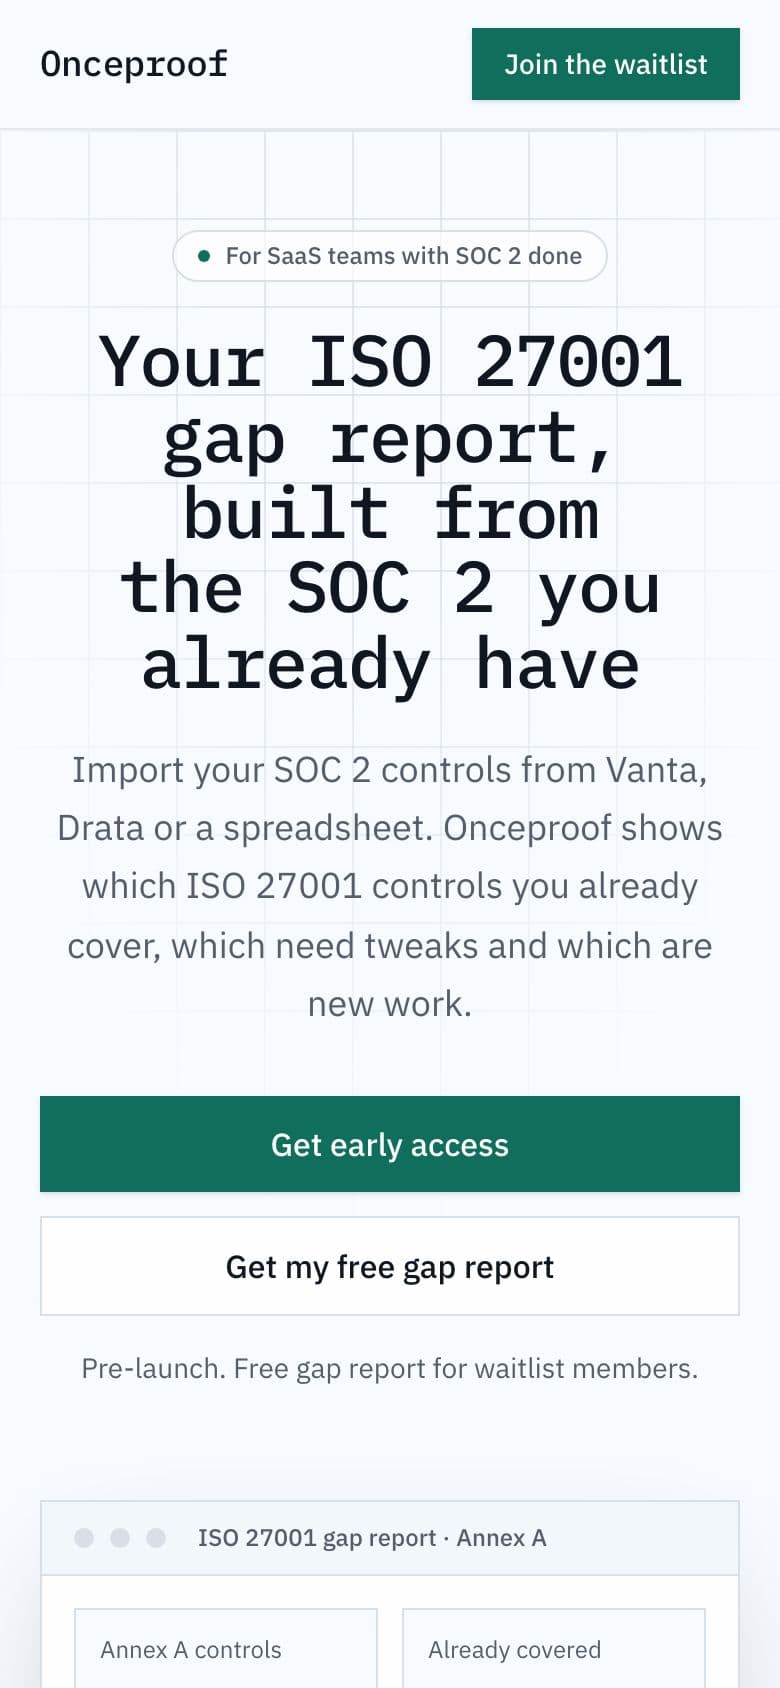
Your ISO 27001 gap report, built from the SOC 2 you already have
The posts come from teams with SOC 2 done and ISO 27001 coming next. The headline starts from that point and offers a gap report built on work they already have, so it answers the fear of starting over without promising anything this example cannot show.
Words it borrows from real posts:
- “build the same controls twice”
- “keep asking about ISO 27001”
- “security, compliance and internal audit”
Sections, in order (11)
- Navigation: It gives quick jumps to the parts a compliance lead checks first, how it works and pricing, and keeps a waitlist button in view the whole time.
- Hero: It names who it is for, SOC 2 done, and shows a sample gap report sorted into covered, tweak and new. The visitor sees the promised output before reading anything else.
- Problem: It plays back the pains in the posts: rework, buyers waiting on certifications, triple testing, spreadsheets that break. Quotes here should stay close to what people actually wrote.
- How it works: Four plain steps show the work starts from existing SOC 2 controls, not a blank template. That answers the worry about rebuilding before it is raised.
- Features: Each feature maps to one ask in the posts: see the delta, test once for every audit, keep the current tool, and keep one shared record of who tested what.
- Who it's for: It says who should sign up and who should not, including that NIS2 is not supported at launch. Being honest about scope keeps the waitlist made of people the test can learn from.
- Comparison: It sets the idea against the spreadsheet and the consultant, the two options people mention or imply. It compares on reuse and shared testing, the points they asked about.
- Pricing: It states one flat price and leads with the free gap report. The note says nothing is charged before confirmation, which fits a page testing an idea that is not built yet.
- FAQ: It answers the objections a careful compliance lead would raise: another tool, framework coverage, cost, data handling and whether an auditor will accept the work.
- Final call to action: It closes on the posts' own phrase about building the same controls twice and repeats the free gap report offer, so the last thing read is the problem and the next step.
- Footer: One line restates the core idea, control once and reuse for every audit, so the page ends on what the product is meant to do.
Price
- Gap Report: Free
- Onceproof: $500 a month
The free gap report lets people see their ISO 27001 delta before paying, which is the first thing the posts want to know. The single $500 a month plan covers every framework, so the many-audits-a-year problem never means a growing bill. On this test page it measures interest, not sales.
Call to action
The button says Get early access. After the click: Onceproof is almost ready
Get early access is honest for a product that does not exist yet. The click asks only for interest, and the dialog says Onceproof is almost ready. That tells Ghostlaunch whether the idea pulls people without charging them or promising a working tool.
Look
Brand colour #0F6E5C, the “technical” font pair, a light theme.
A deep green reads as steady and trustworthy, which matters to people handling audits and evidence. The technical font pair suits control IDs and tables. A light theme keeps dense mappings easy to scan, like the documents these teams already work in.
The demand behind it
Onceproof was built for a problem people keep posting about: Teams that already have SOC 2 are being asked for ISO 27001 next, and sometimes NIS2 mappings or insurer requirements too. They say they don't want to "build the same controls twice" or have security, compliance and internal audit "testing the same control three times." In heavily regulated industries this means many audits a year, and spreadsheets stop keeping up as the process grows.
“one US prospect wants SOC 2 before procurement moves forward. two others, one here and one in Europe, keep asking about ISO 27001.”
r/grc · 15 Oct 2026 · Read it on Reddit (SOC 2 or ISO 27001 first for a Sydney SaaS startup selling overseas?) “SOC 2 is manageable, but ISO 27001 is coming next and I really don’t want to build the same controls twice.”
r/soc2 · 14 Oct 2026 · Read it on Reddit (What does everyone use for GRC and compliance in 2026?)
Make one for your idea
Describe your idea and see who's asking for it. If you want, Ghostlaunch builds a page like this one and runs the 7-day test.
More SaaS examples
- Postwise · First Customers Finder
- Stallwatch · Signup Drop-off Diagnosis
- Proofkeep · Compliance Evidence Collector
- All SaaS landing page examples